August 21, 2026
Address poisoning
A wallet sent $2M in USDC to a lookalike address it copied from its own transfer history.
- sent to
- 0xF0e6A49668dE1195B931A3717c9cc36fc19721aF
- intended
- 0xF0e67A1896E814E30c011e36174de28CAA9Ab1aF
Scam Sniffer finds scam and malware sites, monitors Ethereum for thefts and exploits, and lists the addresses behind them. Wallets, exchanges, and security platforms query the same data over our API.
420K+ domains · 61K+ addresses · Ethereum monitored block by block
Queried by wallets, exchanges & security teams
Large-scale scanning finds scam infrastructure, on-chain monitoring finds the addresses behind thefts and exploits, and every entry is verified before it ships.
Team
What they do with it
Endpoints
Check a link or a recipient address before the user signs or sends. Warn on scam sites and drainer contracts, and show the address label in the warning.
site check
address check
Screen deposit and withdrawal addresses against drainer and exploiter addresses. Batch-check addresses during review, and get the label and source transaction where known.
address check
address resolver
Merge the feed into your own detection, tracing, and case work, with bulk exports and labels and categories for triage.
blocklist export
data license
API
Lookups return BLOCKED or PASSED. Where we know more, the address resolver adds the label, category, and source transaction.
$ curl "$SCAMSNIFFER_API/site/check?url=https://app-sushii-swap.com" \
-H "x-api-key: $SCAMSNIFFER_KEY"
{
"url": "https://app-sushii-swap.com",
"host": "app-sushii-swap.com",
"status": "BLOCKED"
}
$ curl "$SCAMSNIFFER_API/v2/blacklist/domain/byAddress?address=0x8296721489d0a7e934edd66ea27159b1c88a42e5" \
-H "x-api-key: $SCAMSNIFFER_KEY"
{
"label": ["X100 Governance Attacker: Fund Holder"],
"category": "exploit",
"id": "x100-exploit-2026-10-24",
"domains": [],
"transaction": "0x38c60844f1923d53fdce7d99e9bc2a2d8c73a08e793341dfbb479f8cc74d81d0",
"chain": 1
}
Cases from our public alert feed on X, each verified on-chain. Follow @realScamSniffer
August 21, 2026
A wallet sent $2M in USDC to a lookalike address it copied from its own transfer history.
August 12, 2026
Two wallets were emptied in 15 minutes. DAI, WBTC, aUSDC, LDO, sUSDe, and ETH all went to a fresh address.
March 16, 2026
A wallet lost $1.77M in USDC after signing a phishing permit (gasless approval) signature on Ethereum. One transaction moved it all.
Automated detection is set to catch as much as possible, so it also flags things that turn out to be legitimate. Nothing reaches the blocklist until it has been verified.
01
Scanners read pages and newly seen domains. On-chain monitors check each Ethereum block. Both produce candidates, not verdicts.
02
Automated checks first, human review when a case is not clear-cut. Only verified entries are listed.
03
Entries carry a label, a category, and the source transaction where known. Reported false positives are reviewed and removed from the blocklists.
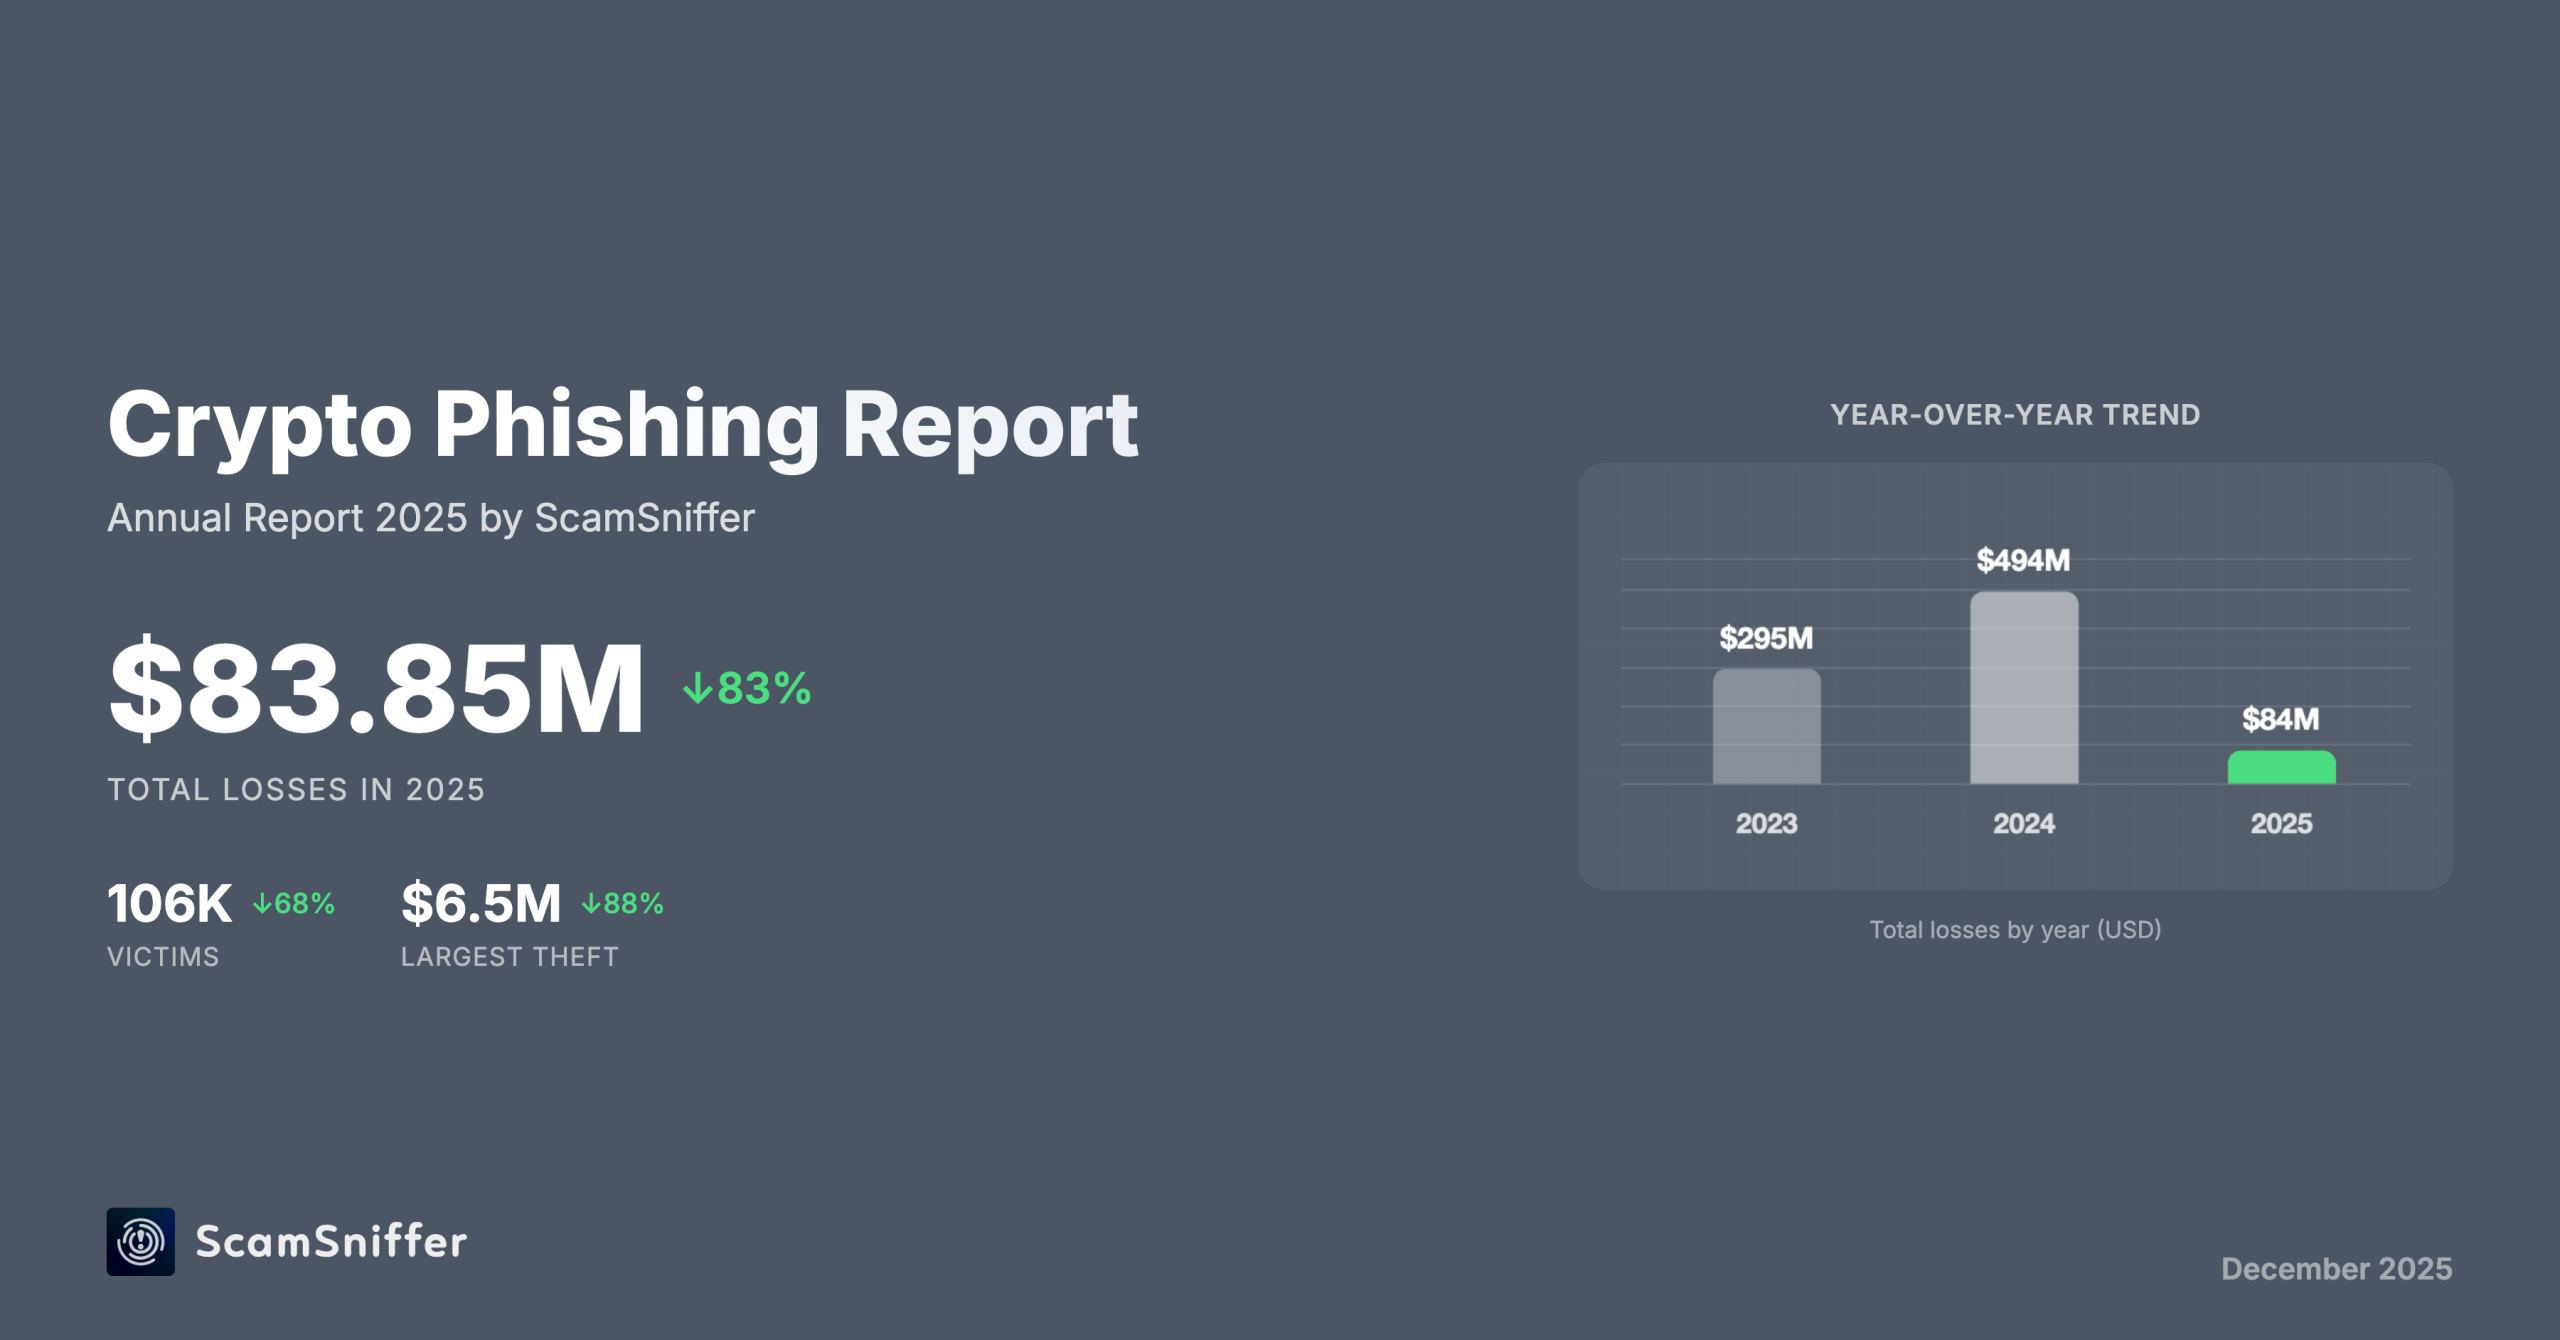
We publish drainer-family research, victim statistics, and annual reports — free, from the same pipeline that powers the blocklists. Industry media regularly cite them.
Pricing
$0
The public scam database on GitHub. Best for research, hobby projects, and evaluation.
from $999 /month
Lookups over API for a single product. Priced by query volume.
Labels, bulk exports, and SLAs are part of Enterprise.
Get an API keyCustom
For wallets, exchanges, chains, and security platforms. Priced by usage and scope.
Tell us what you need to block or screen, and we'll run the data against your own examples.
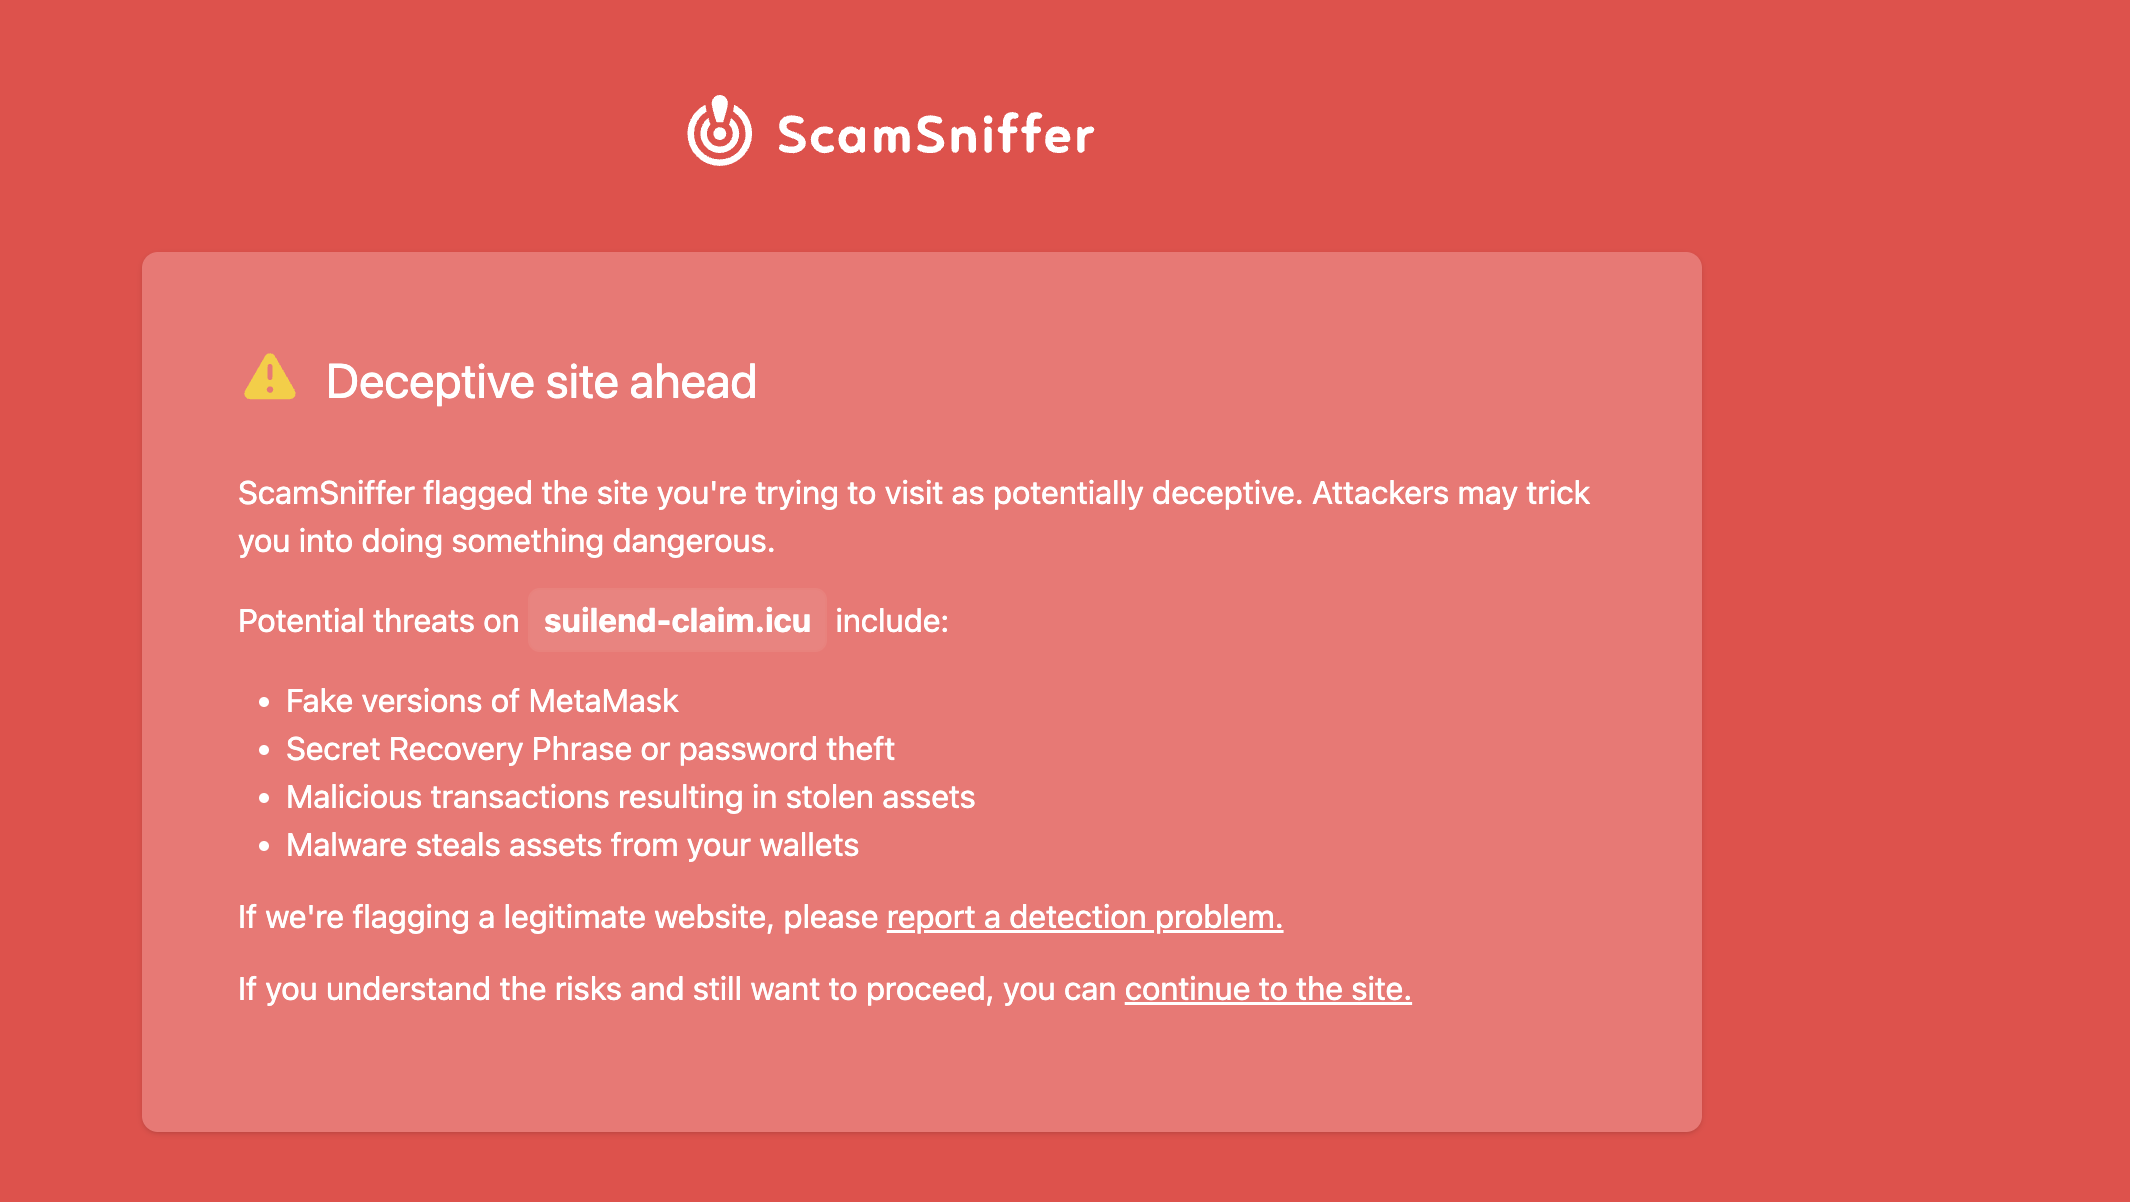
The Scam Sniffer extension warns you when a site or address is on our blocklists, the same data the wallets above query.